Itheon Log Analyzer is a centralized syslog collection, search and analysis platform. It manages remote hosts' log forwarding, ingests the stream in real time, and indexes every event for fast search — giving IT and security teams a single console for live log viewing, reporting, alerting and security investigation.
From one dashboard, teams can search millions of indexed events in seconds, build saved investigation streams the whole team shares, trace suspicious IP addresses, and get notified the moment a threshold is breached.
The first release of Itheon Log Analyzer ships as a complete platform: live log search, dashboards, saved streams, threshold alerting, reports, audit & security, AD analytics, and IP intelligence.
Everything your team needs to collect, search, and act on log data — in one console.
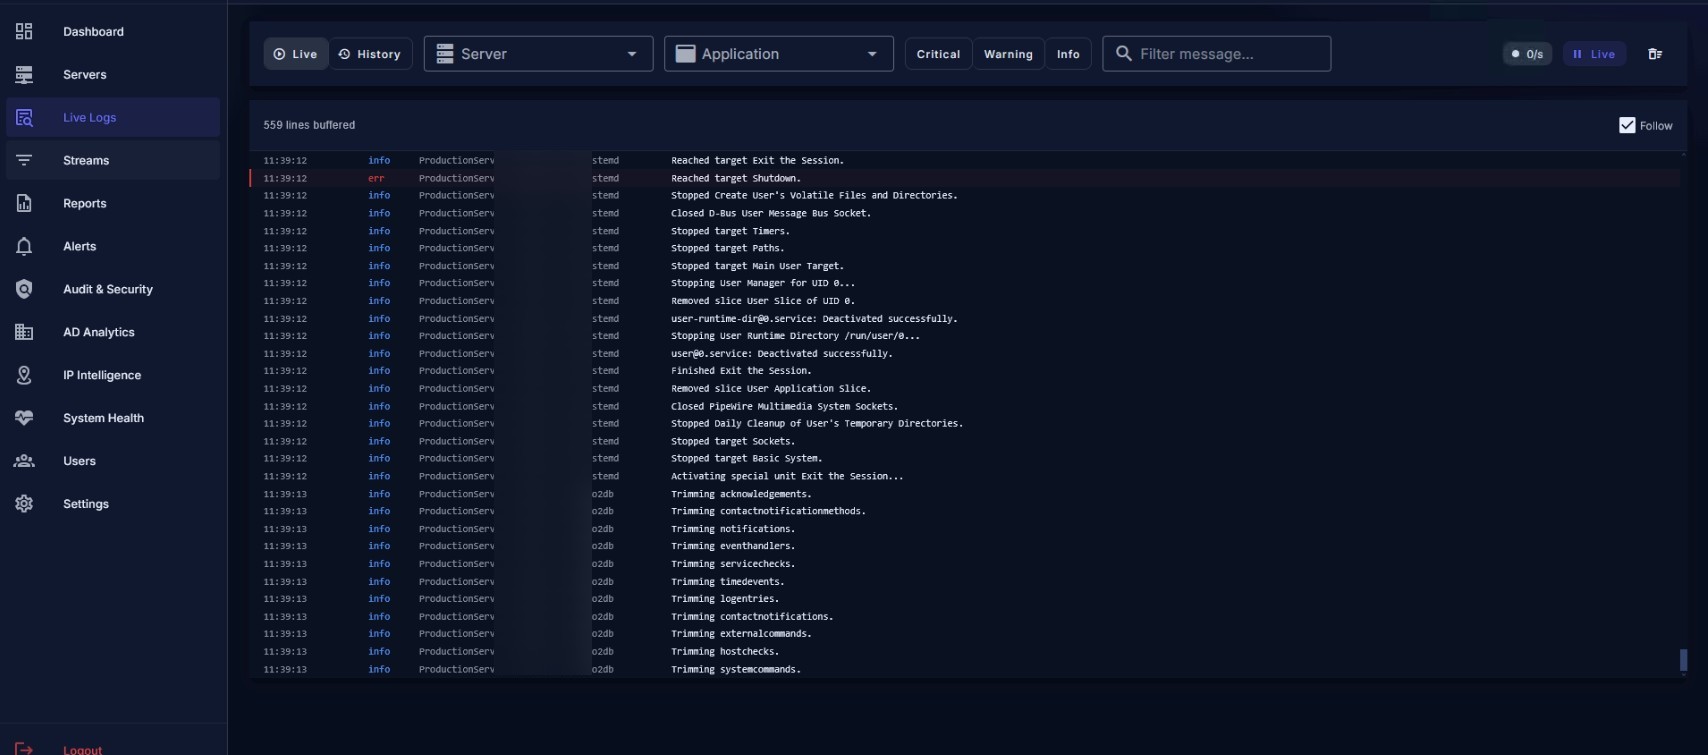
Filter and search the full indexed log corpus by server, application, severity, and free text, with results in seconds.
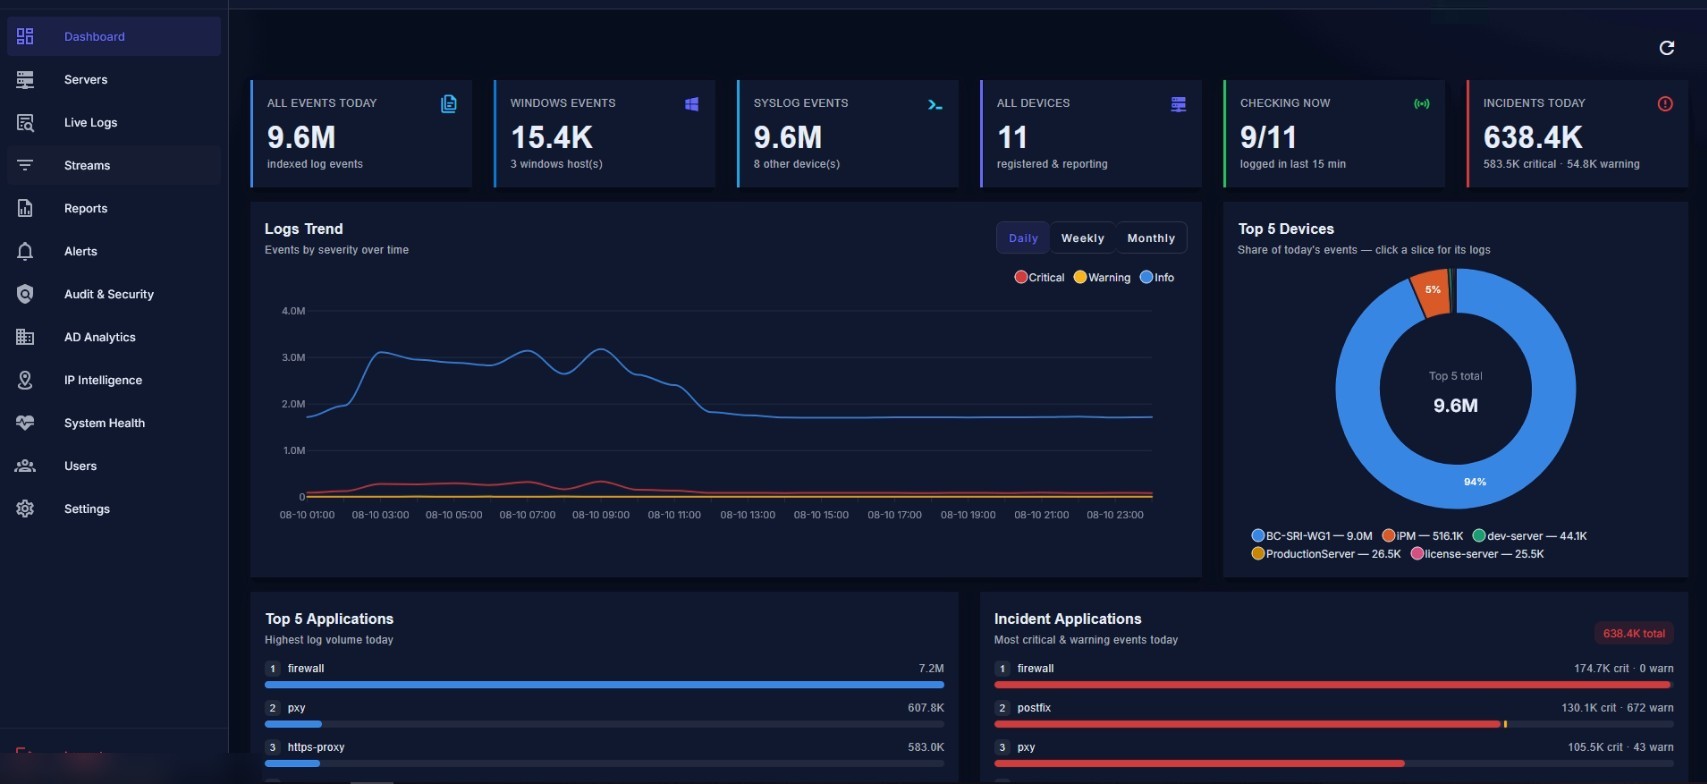
A daily situational summary — event volume, top devices, top applications, and today's incidents at a glance.
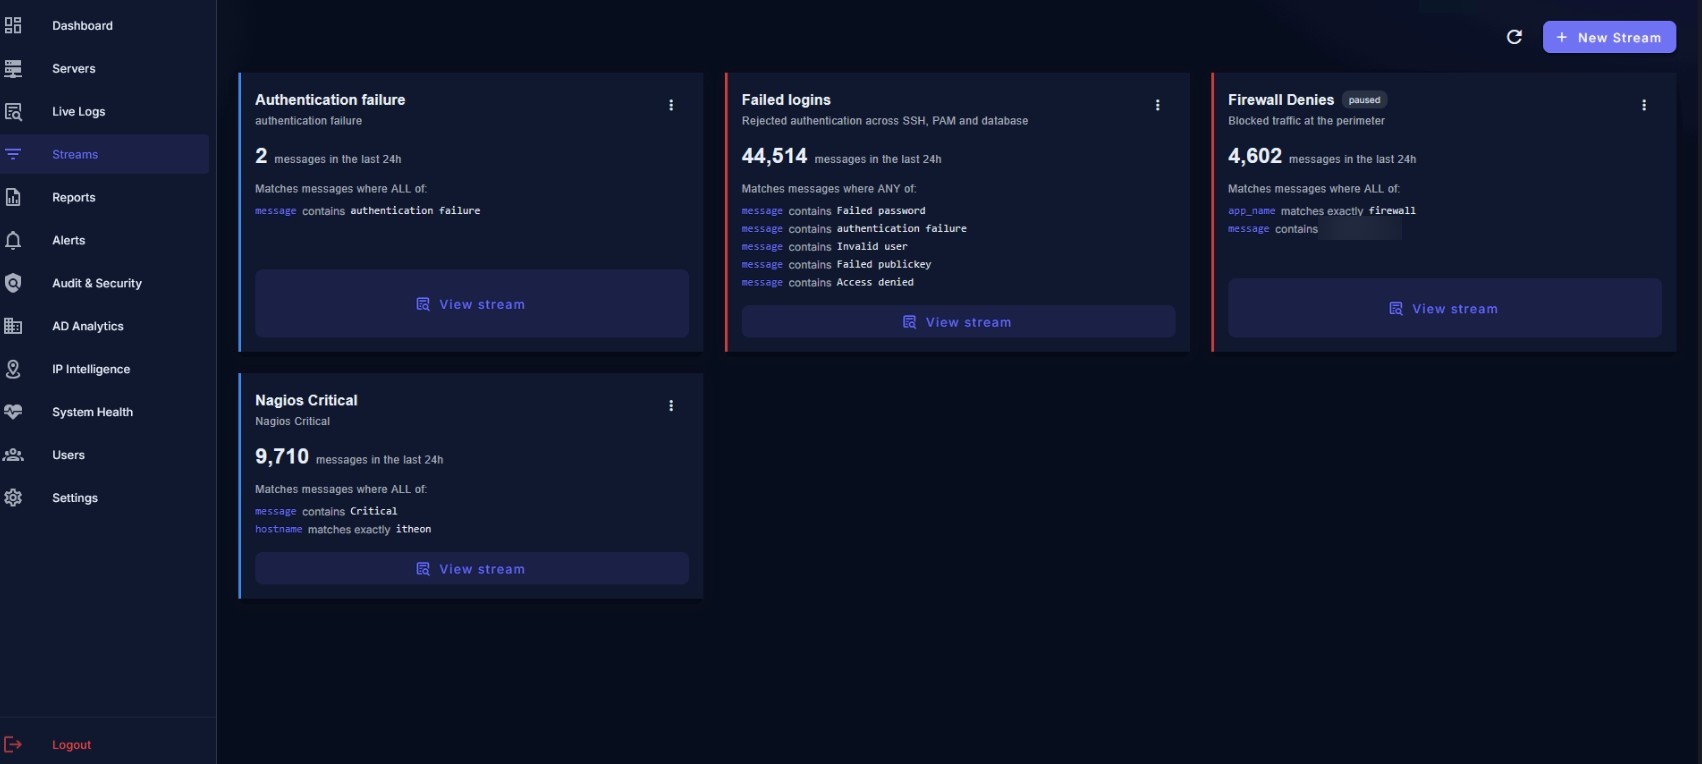
Save rule-based views over the log corpus so the whole team shares the same live investigation.
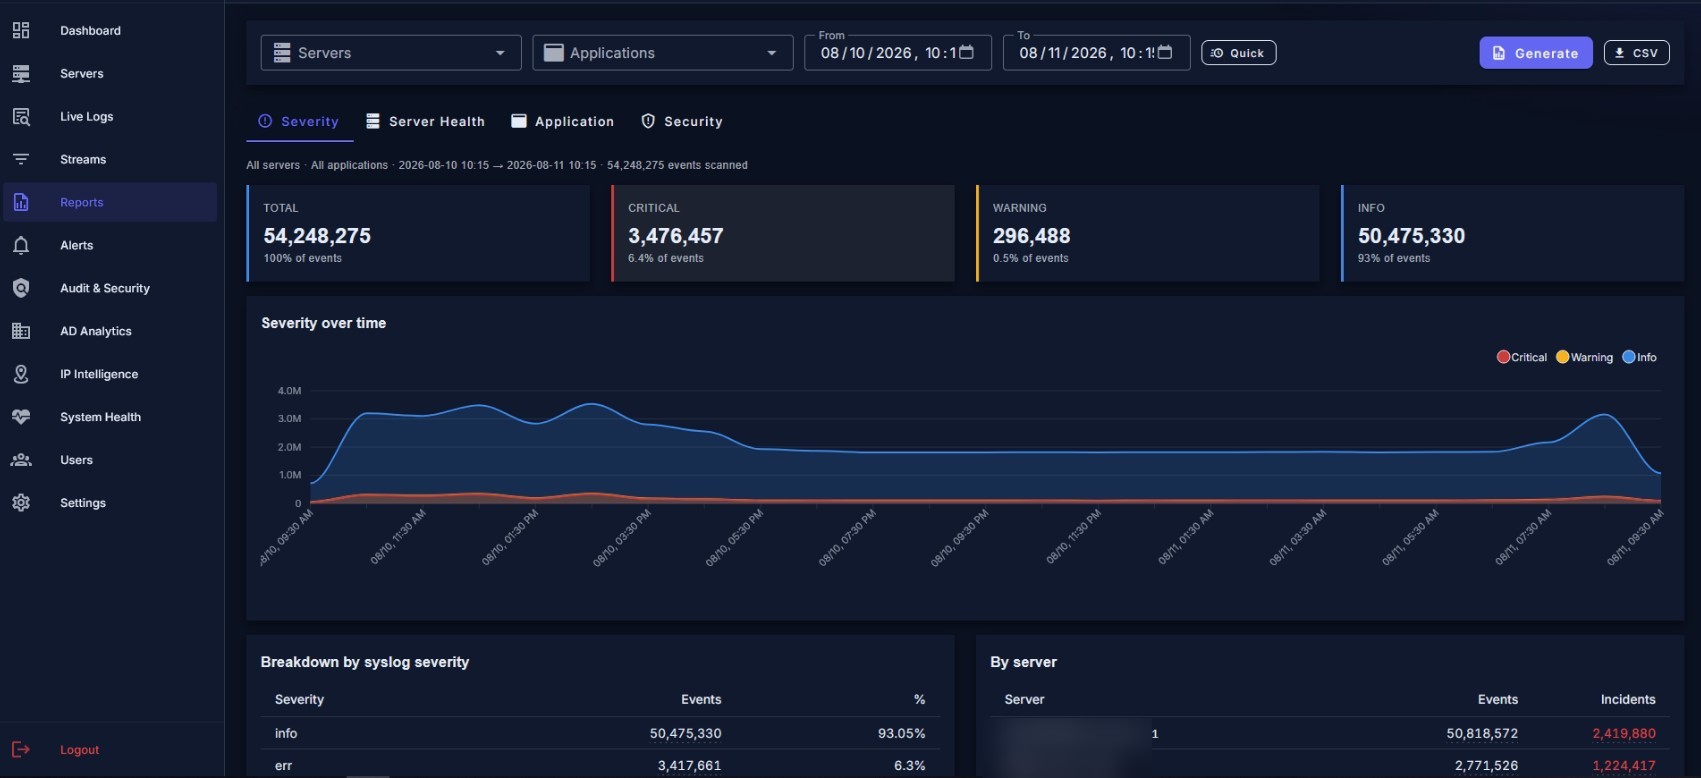
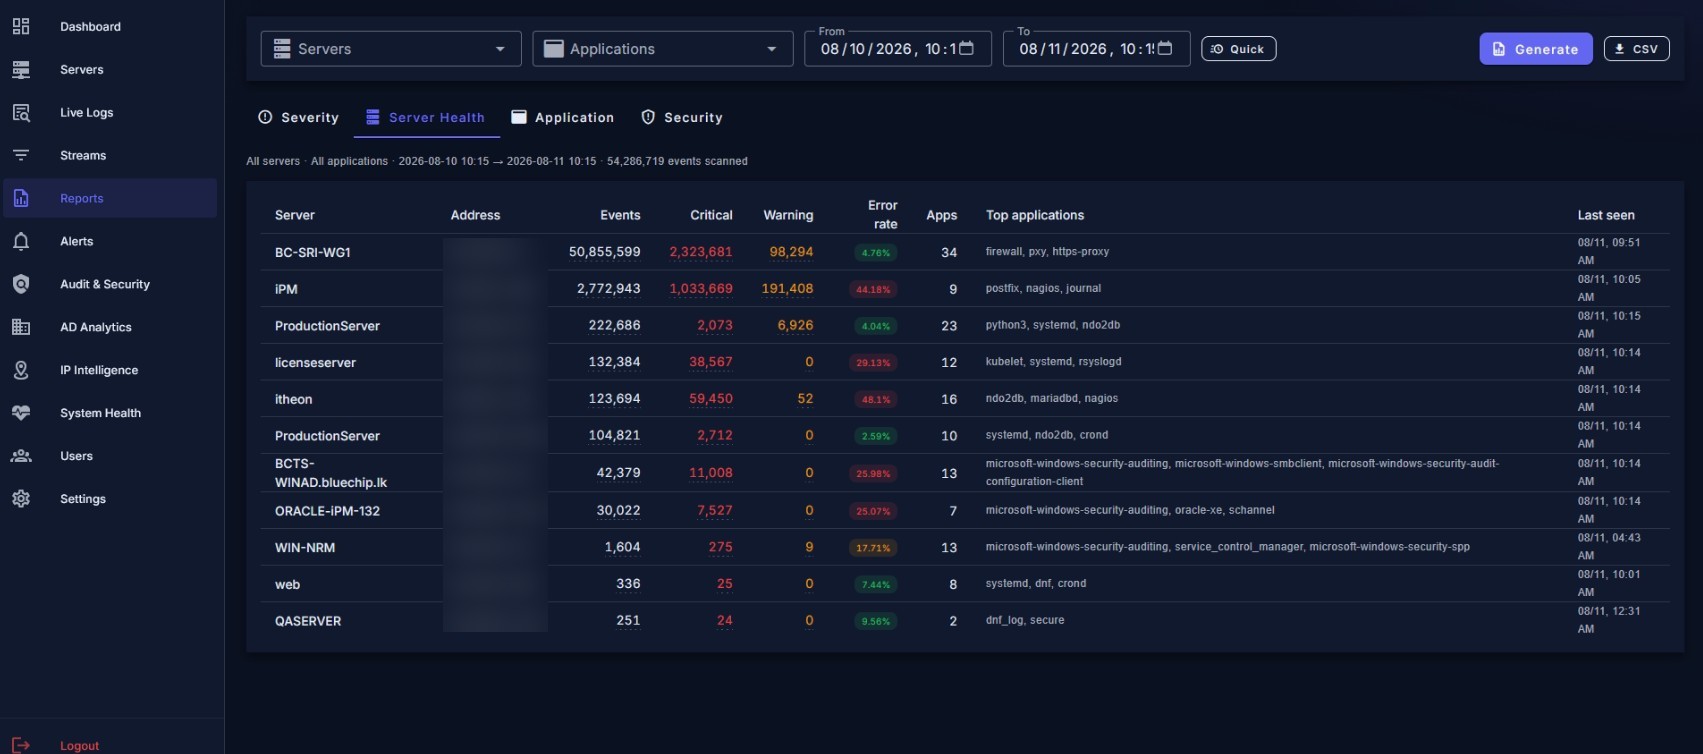
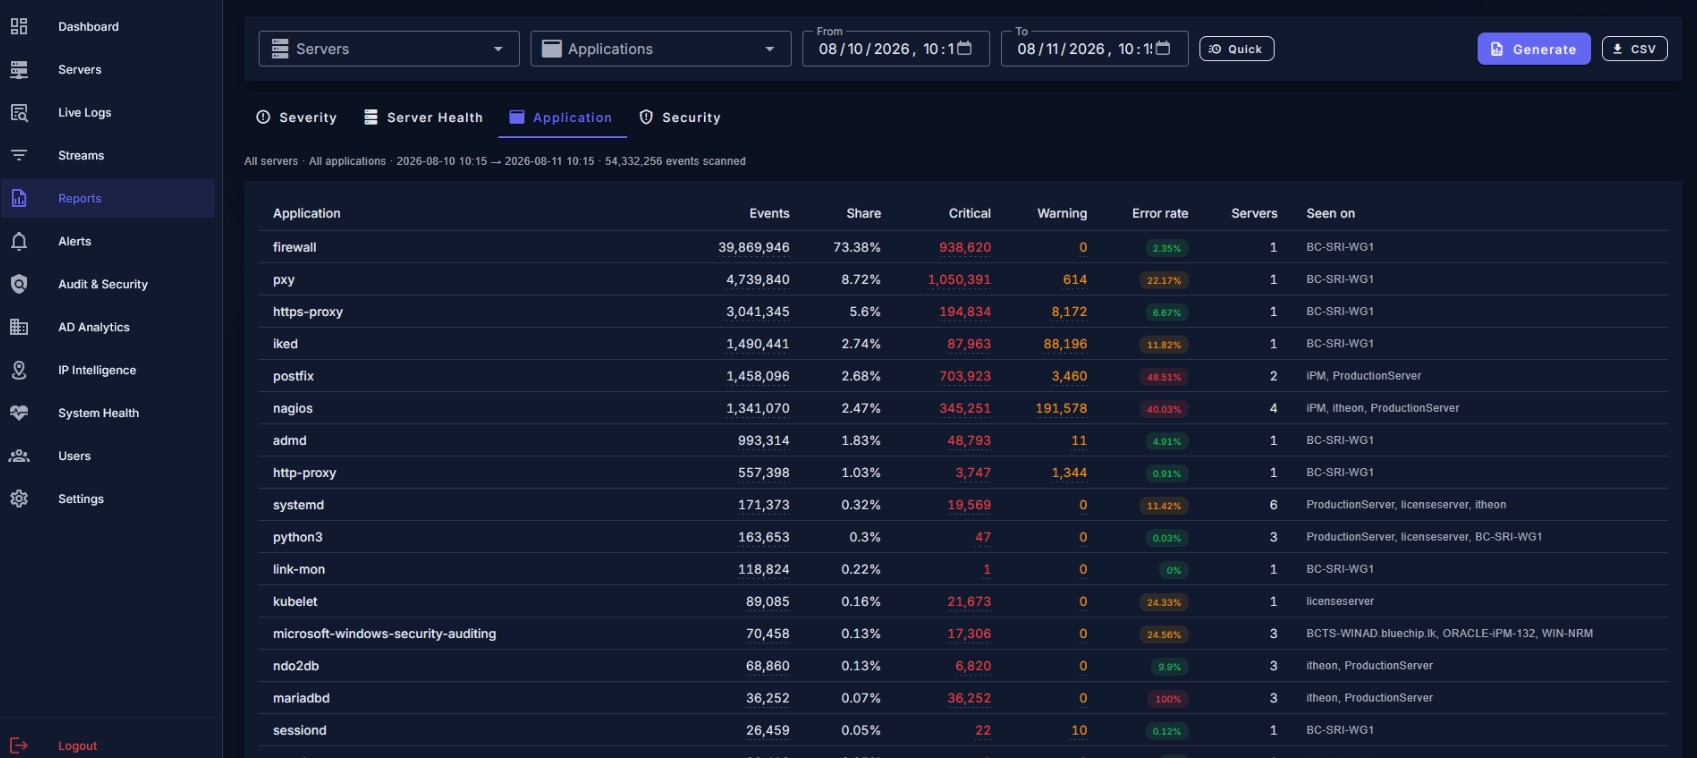
Severity, server health, application, and security reports, all built from the same filter set.
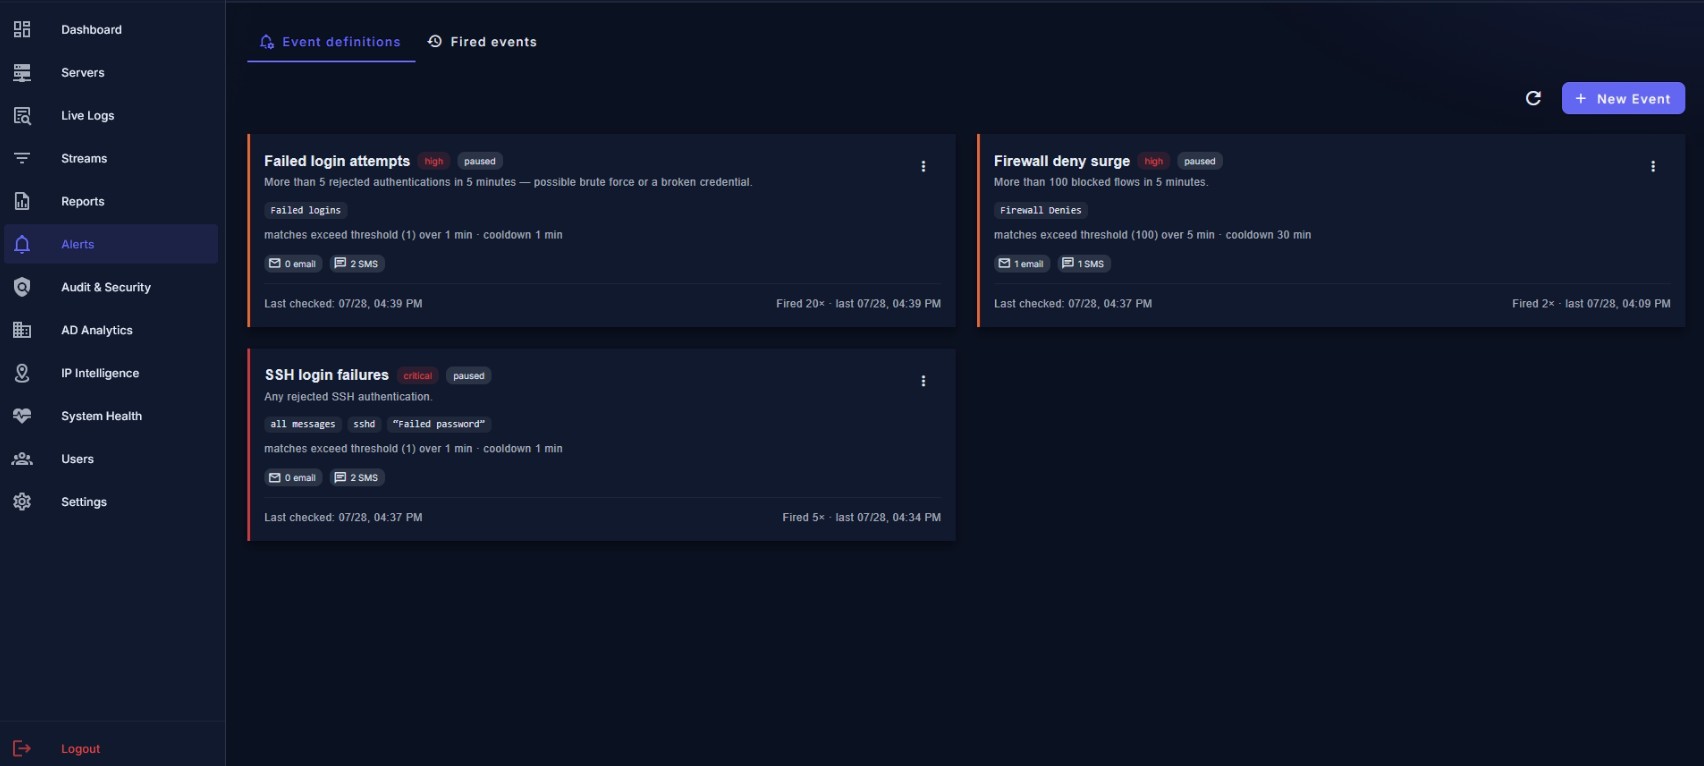
Define what to watch, when to fire, and who to notify, with cooldowns so one incident doesn't page anyone twice.
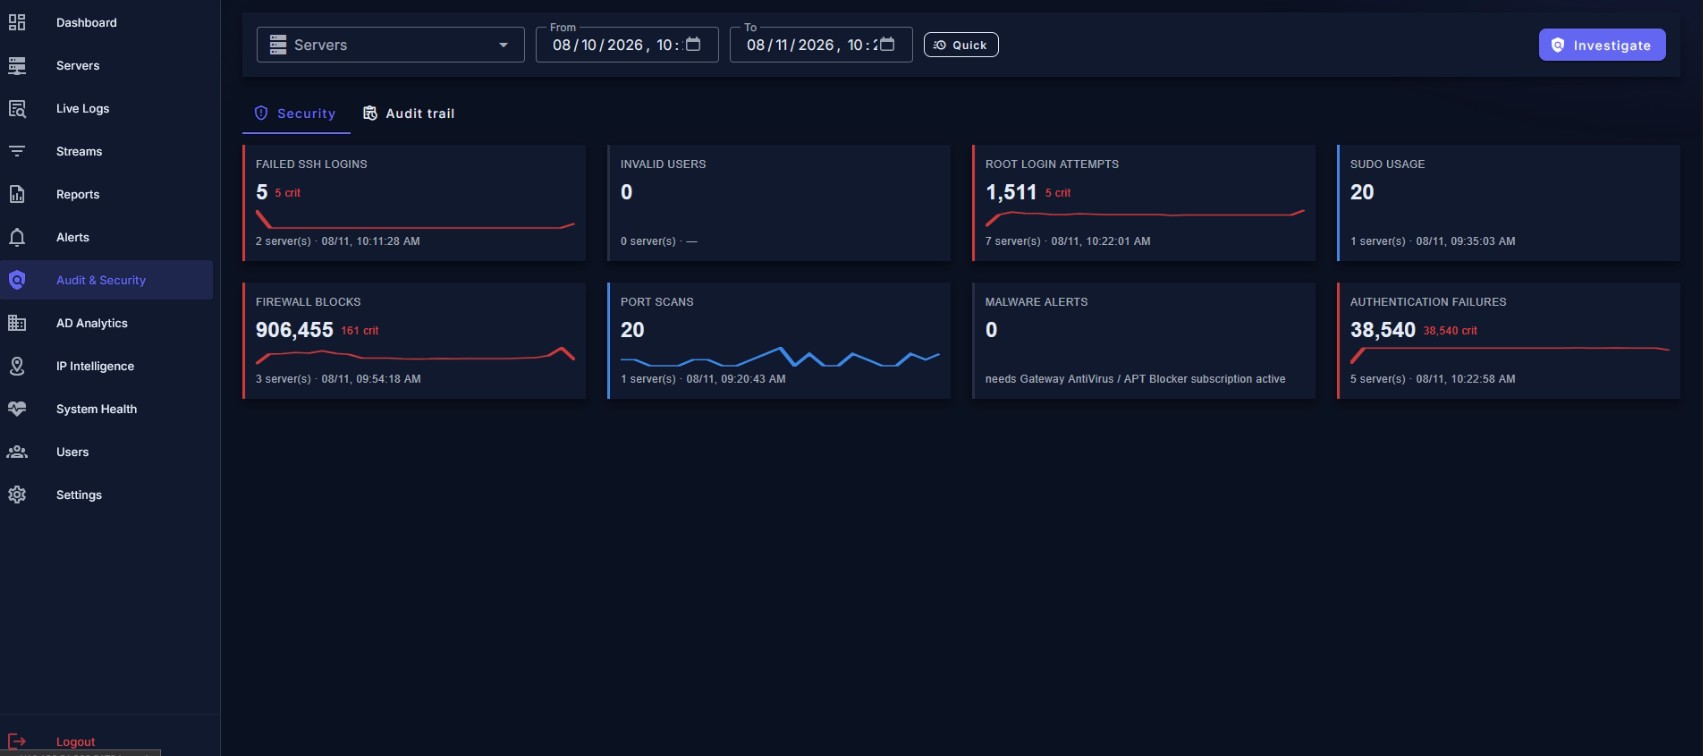
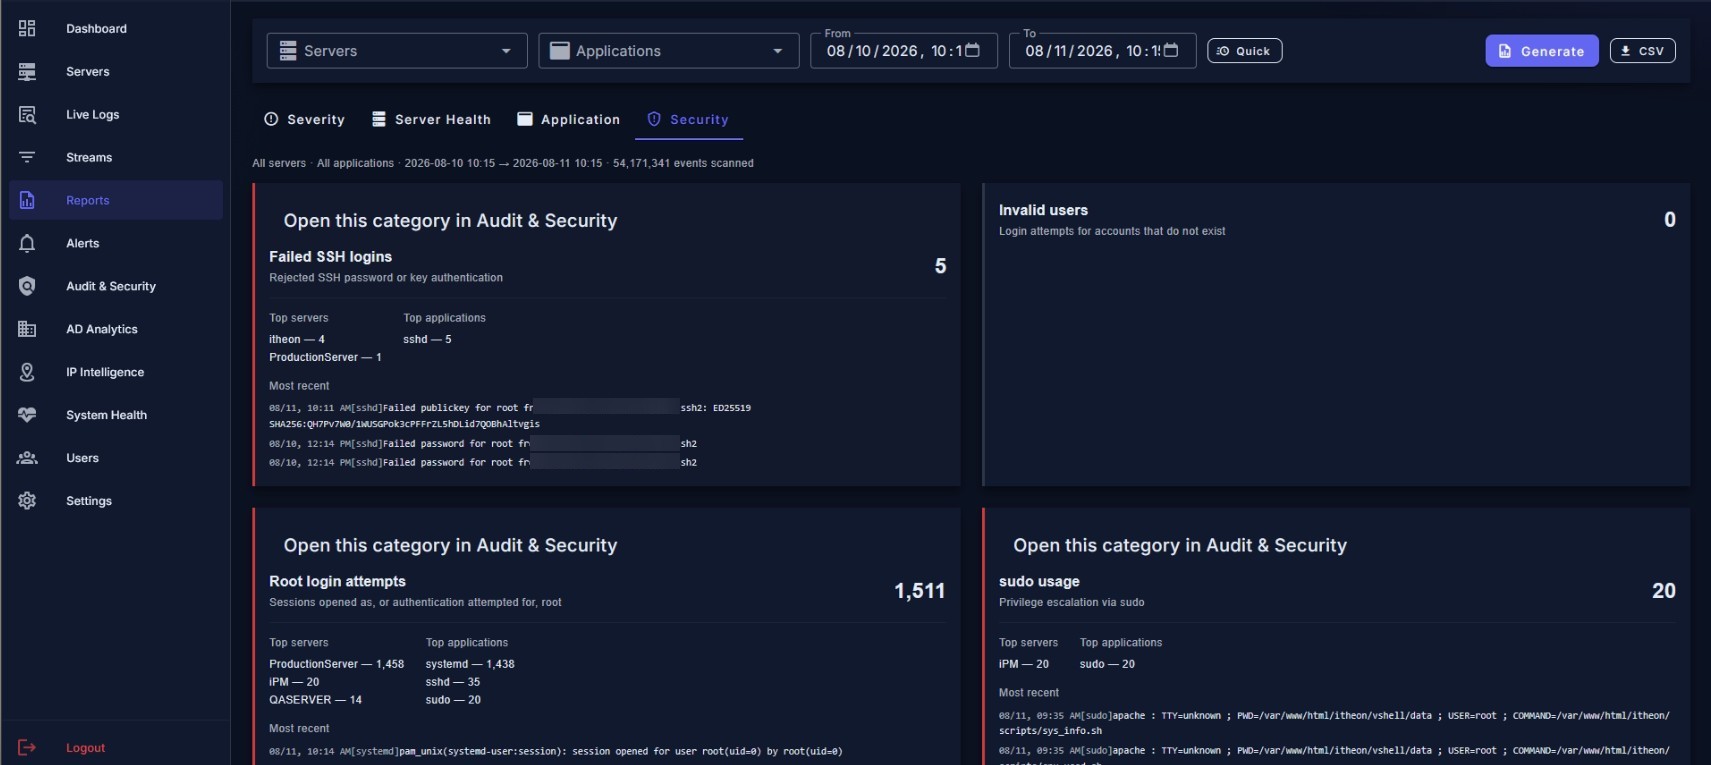
Failed logins, root attempts, sudo usage, and port scans, each signal drillable down to the actor and target.
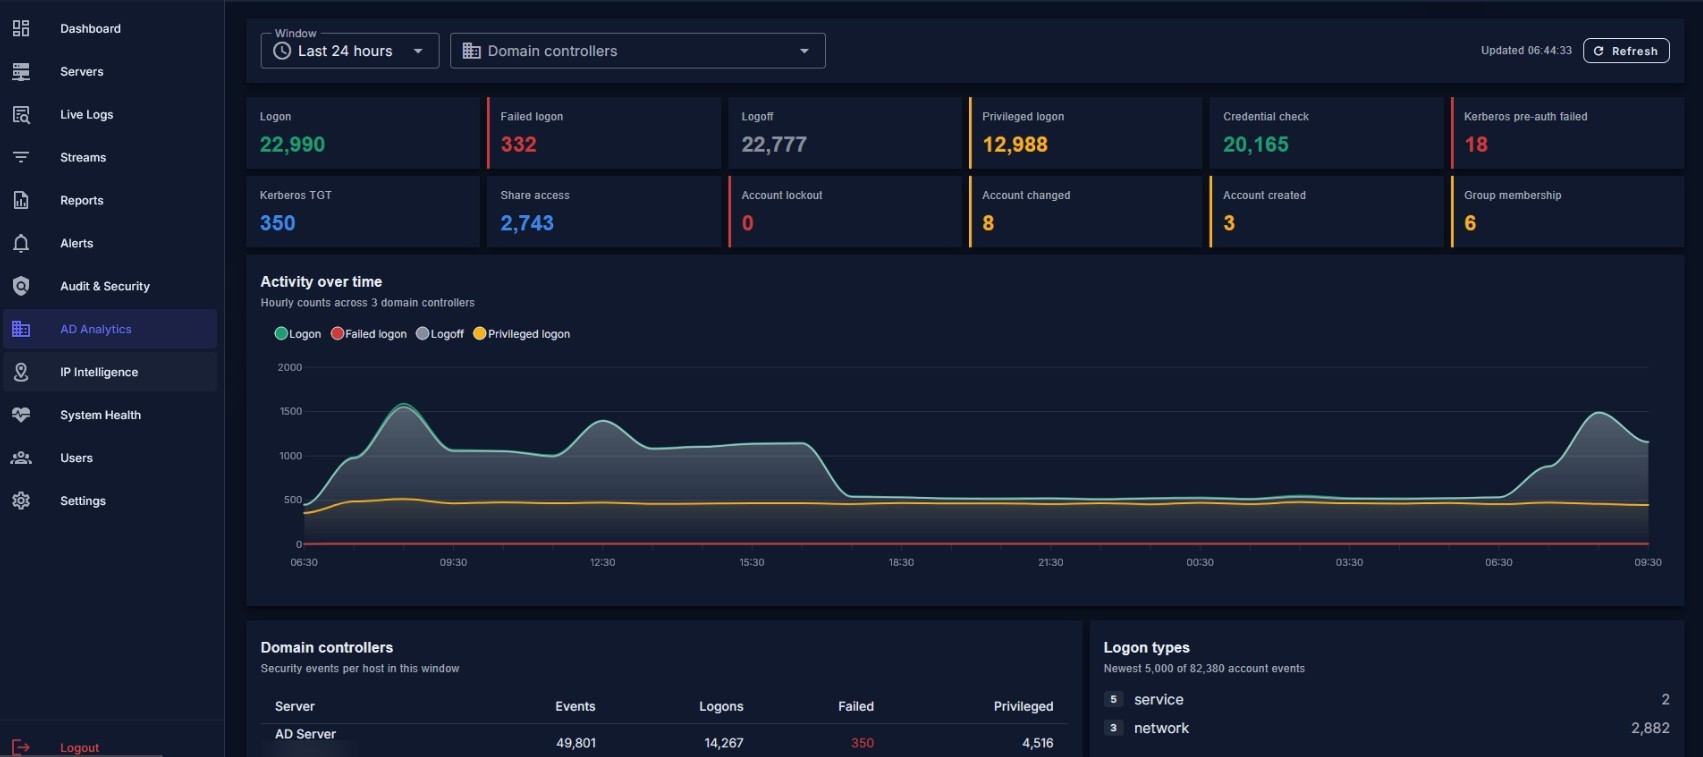
Track Active Directory logons, failed logons, privileged access, and account changes across every domain controller.
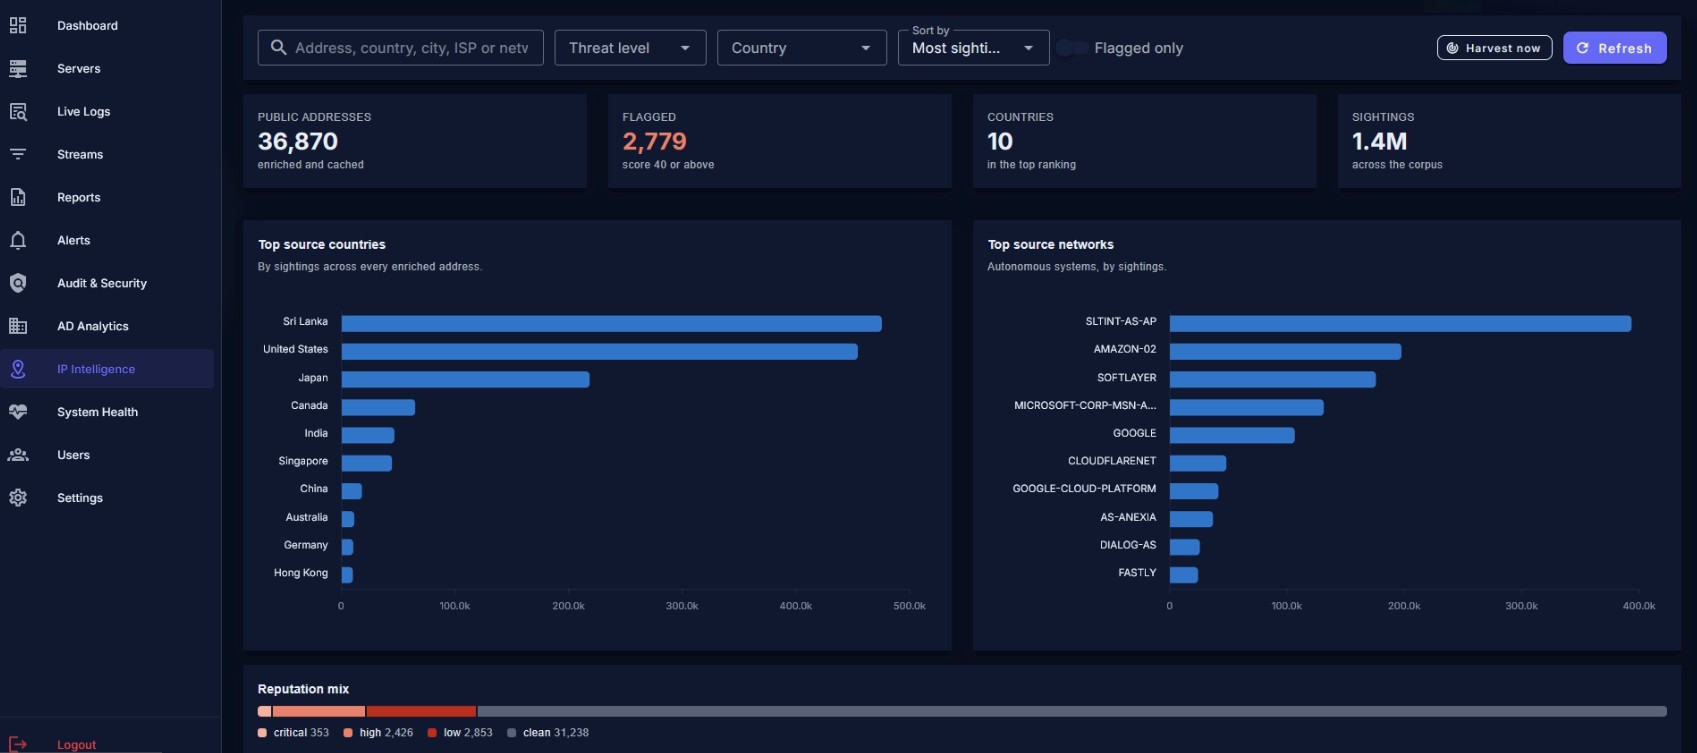
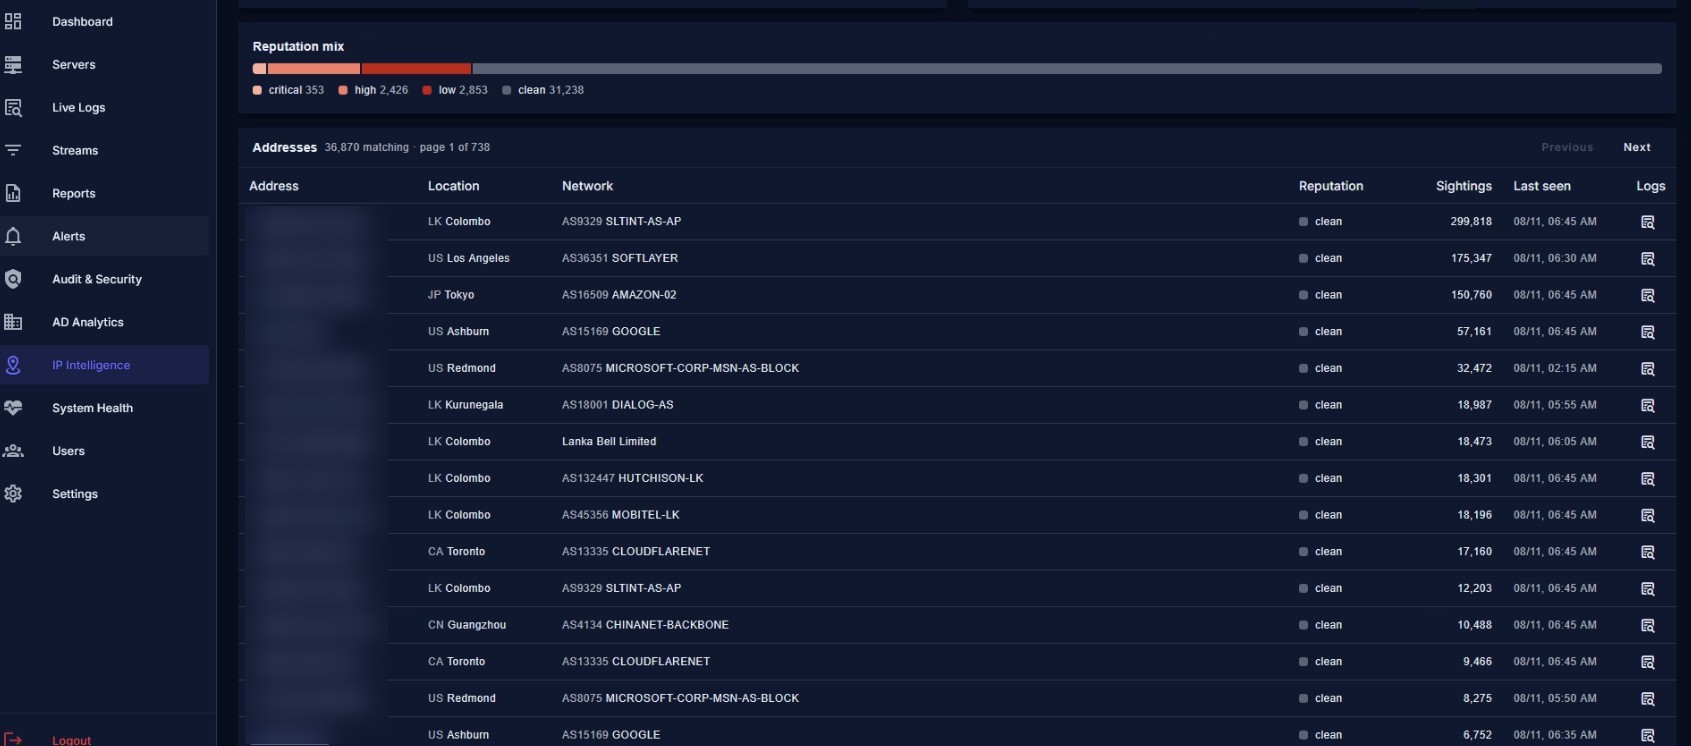
Enrich every public IP address in your logs with geolocation, network ownership, and threat reputation.
A closer look at reporting, streams, and threat intelligence inside the console.
Rule-driven alerting over the incoming log stream, so IT teams are notified the moment something needs attention.
Aggregated reporting over the indexed log corpus, all sharing the same server, application, and time-window filters.
Turn scattered server logs into a searchable, actionable source of truth.
Bring logs from every server into one searchable console instead of signing into boxes one by one.
Rule-based alerts and saved streams surface problems the moment they start, not after a support ticket.
Audit & Security and IP Intelligence turn raw log noise into a real forensic trail.
Rsyslog install, discovery, and forwarding are all managed remotely over SSH, without touching each box by hand.
Assign specific servers to specific users, so every team only ever sees the logs relevant to them.
Automatic retention and archiving keep only what you need, compressing or deleting the rest on schedule.